


Enterprise AI has moved past the stage where governance can be handled by a policy document and an annual compliance review. AI is now embedded inside applications, connected to enterprise data, making recommendations, calling tools, and increasingly taking actions across business systems.
The scale of that change is significant. Gartner forecasts that 40% of enterprise applications will feature task-specific AI agents by the end of 2026, up from less than 5% in 2025. Once AI can update CRM records, approve workflow steps, interact with customers, or coordinate other systems, governance has to control what the application can do, not simply what the model can say.

That is why we define AI Governance for Enterprise Applications as an engineering and operating system for controlling AI across its entire lifecycle: data, models, prompts, retrieval, tools, permissions, evaluation, deployment, monitoring, incidents, and accountability.
The strongest governance programs do not slow AI development down. They remove ambiguity about what teams are allowed to build, what evidence is required before deployment, and which controls must remain active once the system reaches production.
Let’s dive deeper into how AI Governance for Enterprise Applications should work in practice, which controls matter most, and how enterprises can turn governance from a compliance bottleneck into infrastructure for scaling AI safely.
What Is AI Governance for Enterprise Applications?

AI Governance for Enterprise Applications is the framework of technical controls, organizational responsibilities, policies, evaluation processes, and audit mechanisms used to manage how AI applications are built, accessed, deployed, monitored, and changed.
The important word is applications. A production AI system is rarely just a model. It may contain foundation or specialized models, enterprise data and RAG pipelines, prompts, business tools, AI agents, external model providers, user permissions, approval workflows, vector stores, and monitoring infrastructure.
Governance that focuses exclusively on “the model” therefore misses most of the system. A customer-service assistant can use an approved LLM and still expose confidential data through a badly configured retrieval layer. An agent can pass every accuracy test and still create operational risk if it receives excessive write permissions. A model can behave safely at launch and become unsuitable six months later because its provider, prompt, data, or connected workflow has changed.
AI Governance for Enterprise Applications must therefore govern the complete execution path rather than treating individual models as isolated assets.
Read more: AI Implementation Roadmap: A Step-by-Step Enterprise Guide
Why AI Governance Became a 2026 Enterprise Priority
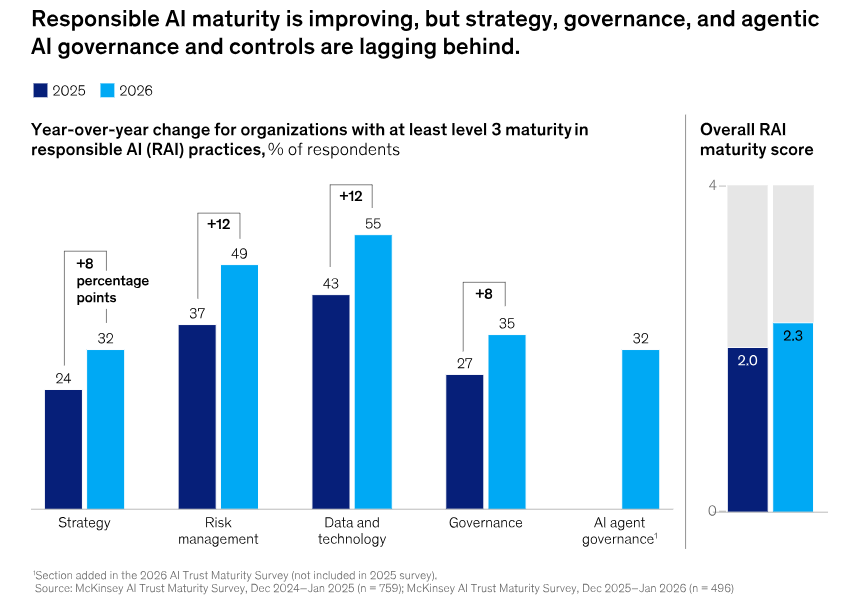
AI adoption is moving faster than governance maturity. McKinsey's 2026 AI Trust Maturity Survey found that only about 30% of organizations reached maturity level three or higher in strategy, governance, and agentic-AI governance. Nearly two-thirds cited security and risk concerns as the top barrier to fully scaling agentic AI, while 74% identified inaccuracy and 72% cybersecurity as highly relevant AI risks.
The problem becomes more significant as autonomy increases. Traditional business software executes logic developers explicitly wrote. AI applications can make decisions based on probabilistic model outputs, retrieved information, tool descriptions, external providers, and user inputs that developers did not predict in advance.
The answer is not to eliminate uncertainty. The answer is to define where uncertainty is acceptable and where deterministic controls must take over. That principle should sit at the center of AI Governance for Enterprise Applications.
AI Governance Is a Control Plane, Not a Policy Binder
The most useful way to think about AI Governance for Enterprise Applications is as a control plane running across the AI application stack.
Business Policy / Risk Appetite
│
▼
AI Governance Layer
│
┌────────────┼───────────────┐
│ │ │
▼ ▼ ▼
Identity Data Policy Model Policy
│ │ │
└────────────┼───────────────┘
▼
Enterprise AI App
│
┌────────────┼─────────────┐
▼ ▼ ▼
RAG Models Agents
│ │ │
▼ ▼ ▼
Sources Outputs Tools / APIs
│ │
└──────┬──────┘
▼
Human Approval
│
▼
Business Action
│
▼
Trace / Audit Log
Policies still matter, but governance becomes operational only when policy can be translated into enforceable system behavior. “Customer PII must not leave our environment” should become an egress control. “Finance agents cannot approve payments above $10,000” should become an execution rule. “Every high-risk recommendation requires human review” should become an approval gate.
This is the gap between AI principles and governance engineering.
The 8 Core Controls of AI Governance for Enterprise Applications

1. Maintain an Enterprise AI Inventory
You cannot govern systems you cannot see. An AI inventory should record every material AI application, including internally developed systems, embedded SaaS AI, vendor copilots, third-party APIs, and autonomous agents.
A useful record should capture:
| Field | Example |
| Application | Claims Review Agent |
| Business owner | Insurance Operations |
| Technical owner | AI Platform Team |
| Use case | Claims recommendation |
| Models | Approved enterprise LLM |
| Data | Customer records + policy repository |
| External vendors | Model provider |
| Actions | Read claims, recommend outcome |
| Risk tier | High |
| Human oversight | Required |
| Production status | Active |
The inventory should be dynamic. A system that changes models, adds a new source of sensitive data, or gains a tool capable of modifying enterprise records may require reassessment.
This is why AI Governance for Enterprise Applications has to connect directly with deployment and change management rather than live solely inside Legal or Compliance.
2. Classify Applications by Risk, Not by AI Technology
Do not assign the same governance requirements to a marketing copy assistant and a loan-decision system. Governance should scale with impact, autonomy, and authority.
A practical risk model should consider business impact, sensitivity of data, reversibility of actions, regulatory exposure, model uncertainty, number of affected users, third-party dependencies, and required human oversight.
A low-risk summarization assistant may need standard privacy, logging, and quality controls. An agent that modifies financial records needs far stronger evaluation, permissions, approval boundaries, monitoring, and incident-response mechanisms.
The NIST AI Risk Management Framework organizes AI risk-management activities around Govern, Map, Measure, and Manage, with governance designed as a cross-cutting function across the lifecycle rather than a final approval step. Its Figure 5 is also a useful visual reference for illustrating how governance connects with risk identification, measurement, and management.
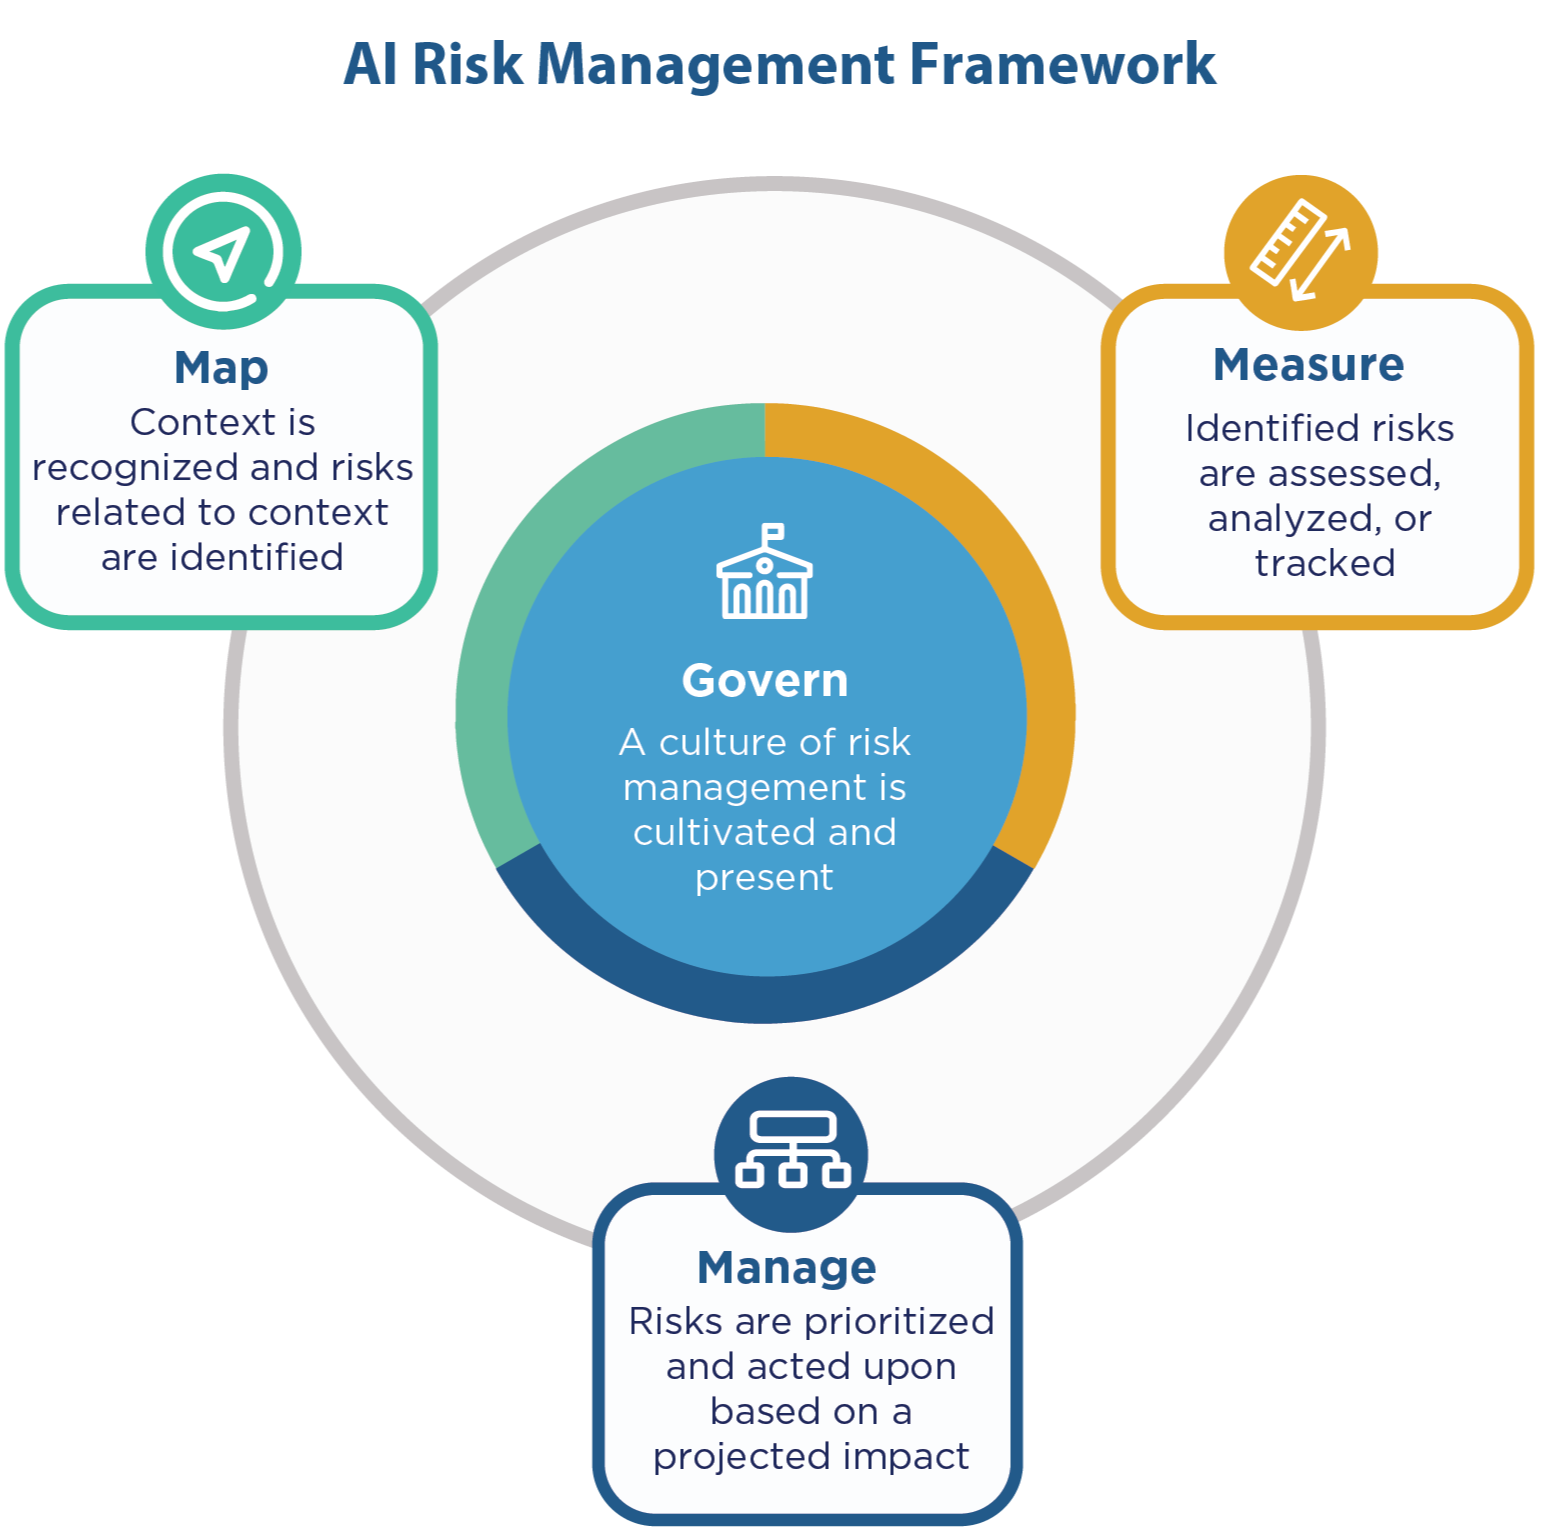
NIST AI Risk management framework (Source: NIST)
3. Govern Data Before It Reaches the Model
Many enterprise AI risks are actually data-governance failures appearing through an AI interface. AI Governance for Enterprise Applications should define which information each application may access, whether it may leave the enterprise boundary, how it is retrieved, and how generated outputs can expose that information.
For RAG systems, authorization should operate before retrieval, not after generation. If a user cannot access a document through the original enterprise repository, semantic search should not create a new path around that restriction.
def retrieve_context(user, query):
allowed_sources = access_policy.sources_for(
user_id=user.id,
roles=user.roles
)
return search(
query=query,
sources=allowed_sources
)
The code is simple, but the architecture principle is critical: retrieval should inherit enterprise authorization rather than bypass it.
4. Control Models and AI Vendors Centrally
One of the fastest ways to lose control of enterprise AI is to let every team independently select models, SaaS AI subscriptions, plugins, and external providers.
AI Governance for Enterprise Applications should separate model policy from application logic wherever possible. The organization needs to know which models are approved, what types of data they may process, where inference takes place, whether prompts are retained, whether data may be reused for training, what model version is active, and what happens when a provider changes or retires a model.
A policy layer might conceptually look like:
application: procurement-assistant
model_policy:
task: document_analysis
data_classification: confidential
allowed_models:
- enterprise-model-a
- private-model-b
public_models:
allowed: false
Illustrative configuration.
The advantage is architectural decoupling: platform and risk teams can update approved models without requiring every product team to rewrite application logic.
Read more: From Software Developer to AI Engineer: Bridging the Gap to Intelligent Solutions
5. Make Evaluation a Release Gate
AI Governance for Enterprise Applications should never rely on someone saying, “The demo looks good.” Material AI systems need measurable release criteria before they reach users or business systems.
| Control area | Example release criterion |
| Accuracy | ≥95% on validated cases |
| Groundedness | ≥98% evidence-supported answers |
| Retrieval | Recall@5 ≥95% |
| Safety | 0 critical-policy violations |
| Security | Prompt-injection test passed |
| Tool use | ≥99% valid tool selection |
| Latency | p95 <4 seconds |
| Cost | <$0.10 per completed task |
| Human review | <15% escalation |
The specific thresholds will vary, but the principle should not: deployment needs evidence.
Evaluation also has to continue after launch because models, prompts, datasets, retrieval systems, tools, and user behavior change. Governance should therefore become part of CI/CD and LLMOps rather than a one-time QA exercise.
6. Govern What AI Agents Are Allowed to Do
Agentic AI changes governance because applications can move from generating information to executing actions. AI Governance for Enterprise Applications therefore needs an authority model covering the complete trajectory from user intent through retrieval, tool selection, API calls, and business-system changes.
| Authority level | Example |
| Read | Retrieve CRM account information |
| Recommend | Suggest a customer discount |
| Prepare | Draft an order modification |
| Execute with approval | Update an opportunity after manager approval |
| Autonomous execute | Perform a bounded, low-risk action |
Permissions should default to least privilege. High-impact actions should be enforced through deterministic controls rather than instructions inside the prompt.
if action.type == "issue_refund":
if action.amount > AUTO_REFUND_LIMIT:
return require_human_approval(action)
if not user.has_permission("refund.execute"):
return deny(action)
return execute(action)
Writing “always ask the manager before a large refund” in the system prompt is not an access-control mechanism.
Gartner has gone even further in 2026, warning that applying uniform governance to every agent regardless of autonomy and access scope can itself cause failure. It predicts that by 2027, 40% of enterprises will demote or decommission autonomous agents because governance gaps are discovered only after production incidents.
Read more: AI Automation vs RPA: Key Differences, Use Cases, and How to Choose
7. Make Every Material AI Decision Traceable
An enterprise should be able to reconstruct what happened after an AI incident. For important systems, the trace should identify the user, application version, model version, active configuration, retrieved evidence, tool calls, arguments, approvals, final action, and applicable policy version.
This is where observability becomes part of AI Governance for Enterprise Applications. A conventional application trace may tell engineers that an API failed; a governed AI trace should help explain why the system reached the decision that triggered that API call.
The OECD AI Principle on Accountability similarly emphasizes lifecycle traceability around datasets, processes, and AI decisions so outputs can be analyzed and questioned when necessary.
8. Plan for Incidents, Rollback, and Retirement
Production AI needs operational emergency controls. AI Governance for Enterprise Applications should give organizations the ability to disable a model or agent, revoke a tool, switch an application to read-only, require human approval, block a data source, suspend a vendor, or restore a previous configuration.
Retirement is equally important. A system should be reassessed or decommissioned when its performance, economics, business process, regulatory position, or risk profile changes materially.
A system that was appropriate for 20 internal users is not automatically appropriate when opened to two million customers.
How Global AI Governance Frameworks Fit Together
Enterprises often ask whether they should “follow NIST, ISO, or the EU AI Act.” That is the wrong framing because the instruments serve different purposes.
| Framework | Practical role |
| NIST AI RMF | Risk-management operating framework |
| ISO/IEC 42001 | Organization-wide AI management system |
| EU AI Act | Legal obligations for relevant EU systems and actors |
| OECD AI Principles | High-level trustworthy-AI principles |
| Security frameworks | Threat-specific technical controls |
ISO/IEC 42001 specifies requirements for establishing, implementing, maintaining, and continually improving an Artificial Intelligence Management System. Unlike a checklist for one application, it gives organizations a management-system structure for governing AI risks and opportunities across the business.
The practical approach is to establish one enterprise governance operating model and map individual frameworks, standards, and regulatory obligations onto it. Creating an isolated governance process for every standard increases administrative complexity without necessarily improving control quality.
What the EU AI Act Means for Enterprise Applications in 2026
For organizations developing or operating AI in Europe, governance now has direct regulatory consequences.
According to the European Commission's AI Act enforcement framework, enforcement powers for several provisions became active on August 2, 2026, including prohibited AI practices, obligations for providers of general-purpose AI models, and transparency requirements for certain systems. Annex III high-risk system rules are scheduled from December 2, 2027, while rules for high-risk systems embedded in regulated products are scheduled from August 2, 2028.
The useful enterprise response is not to create an isolated “EU AI Act project.” Inventory, risk classification, documentation, data governance, human oversight, testing, logging, monitoring, and accountability should already exist inside AI Governance for Enterprise Applications. Regulation then becomes another requirement set mapped onto an operating model that already works.
Read more: Digital Transformation in Banking: Redefining the Future of Finance
Who Should Govern AI in Enterprise?

Enterprise AI governance is inherently cross-functional because different controls live with different teams.
| Role | Primary responsibility |
| Board / Executive Committee | Risk appetite and strategic oversight |
| Business owner | Use-case value and operational accountability |
| AI / Product | Application behavior and evaluation |
| Engineering | Architecture and runtime controls |
| Data | Data quality, lineage, and access |
| Security | Threat modeling and protection |
| Legal / Compliance | Legal and regulatory interpretation |
| Risk / Responsible AI | Governance standards and risk framework |
| Internal Audit | Independent assurance |
Every production AI system should have both a named business owner and technical owner. A central AI governance team can define standards and shared controls, but it should not become the only group capable of approving every prompt or configuration change.
The scalable model is federated governance: centralized standards and platform controls, with application teams responsible for implementing them within defined boundaries.
Policy-as-Code: Turning Governance Into Engineering
Governance becomes easier to scale when key decisions are machine-readable.
application:
id: finance-analysis-agent
owner: finance-operations
risk_tier: high
data_policy:
pii: restricted
cross_border_egress: deny
model_policy:
allow:
- approved-private-model
tools:
erp.read:
permission: allowed
payment.create:
permission: blocked
forecast.publish:
permission: allowed
human_approval: required
evaluation:
groundedness_min: 0.98
critical_errors_allowed: 0
observability:
log_sources: true
log_tool_calls: true
log_approvals: true
Illustrative governance configuration.
This does not eliminate governance committees, security review, or legal judgment. It translates their highest-value decisions into controls applications cannot casually bypass.
That is how governance stops being documentation and becomes infrastructure.
Measuring Whether AI Governance Actually Works

Governance should have KPIs like any other enterprise capability.
Useful measures include AI inventory coverage, risk-assessment coverage, evaluation coverage, policy-violation rate, human-override rate, unauthorized tool-call attempts, incident severity, mean time to contain, audit-trail completeness, vendor/model drift events, and exception-approval volume.
The target is not to maximize approvals. Governance should reduce unmanaged risk while allowing low-risk development to move quickly.
If every small prompt adjustment needs a committee meeting, the organization is over-governed. If an agent can silently change models or acquire new write permissions in production, it is under-governed.
Good AI Governance for Enterprise Applications makes that distinction explicit.
Industry Context Changes the Governance Model

The governance foundation can be shared across an organization, but implementation should vary by risk context.
Banking needs stronger controls around customer data, financial actions, model changes, explainability, and auditability. Healthcare increases the importance of patient privacy, clinical impact, safety, and human review. Education raises student privacy, fairness, academic integrity, and educator authority. Manufacturing may require edge controls, confidence thresholds, equipment-safety boundaries, and rapid escalation when vision or predictive systems drift.
One generic governance checklist will not handle these environments equally well.
Read more: Generative AI in Education: 12 Use Cases and Examples
How SotaAgents Turns Governance Into Runtime Controls

The distinction between governance policy and governance infrastructure becomes even more important with autonomous agents.
SotaAgents is designed around the idea that enterprise AI should operate through a governed platform rather than fragmented subscriptions and disconnected agent deployments. Its public architecture includes workspace model controls, cloud/hybrid/self-hosted/air-gapped deployment, governed tool and MCP integrations, scoped authentication, versioned application components, environment separation, runtime guardrails, tracing, source-level evidence, and human sign-off for sensitive workflows.
A conceptual agent policy could look like:
agent: procurement-assistant
tools:
supplier.search:
access: read
purchase_order.create:
access: execute
approval_required: true
data:
personal_data:
external_egress: deny
runtime:
trace_every_action: true
cite_sources: true
human_override: enabled
Illustrative configuration.
The architectural principle matters more than the syntax: governance should travel with the application into runtime.
How SotaTek Implements AI Governance for Enterprise Applications

For enterprise AI, we do not recommend adding governance as the final project phase before go-live. By then, many of the most important decisions about data, models, providers, integrations, and autonomy have already been made.
A practical delivery sequence is:
| Stage | Governance work |
| Use-case design | Define users, impact, risk, and automation boundaries |
| Architecture | Map data, models, vendors, tools, and permissions |
| Risk classification | Assign control requirements proportional to impact |
| Development | Implement identity, authorization, data boundaries, guardrails |
| Evaluation | Set measurable release criteria |
| Deployment | Enable traces, monitoring, rollback, and incident controls |
| Operations | Reassess models, vendors, data, behavior, and regulations |
SotaTek's AI development capabilities include enterprise integration, model evaluation, access controls, LLMOps, monitoring, explainability, audit trails, and human oversight. The objective is not to make every AI application risk-free. That is impossible. The goal is to make risk visible, measurable, owned, bounded, and recoverable.
Enterprise AI Governance Checklist
Before production, leadership should be able to answer:
- Do we know who owns the system?
- Is it registered in the AI inventory?
- Has its business and risk impact been classified?
- Are all models and external vendors approved?
- Do data permissions survive through retrieval and generation?
- Are users authenticated and authorization boundaries enforced?
- Has the application been tested against representative and adversarial cases?
- Are measurable release thresholds documented?
- Are high-impact actions bounded or subject to human approval?
- Can every material AI decision be reconstructed?
- Can the application be disabled or rolled back quickly?
- Is there a process for reassessment as models, data, and workflows change?
If several answers are no, the application is not governance-ready regardless of how impressive the demo looks.
Conclusion
AI Governance for Enterprise Applications should not be treated as paperwork added after an AI system has already been designed. By that point, many of the most consequential governance decisions—what data the application can access, which models it can use, which tools it can call, and how much authority it receives—have already been made.
The scalable approach is to design governance into the application lifecycle from the beginning: maintain an AI inventory, classify risk, govern data and models, establish release gates, restrict agent authority, trace material actions, require human oversight where consequences justify it, and preserve the ability to roll back or retire the system.
The enterprise that governs AI well is not necessarily the one with the largest policy manual. It is the one where teams can consistently answer three questions: What is this AI allowed to do? What evidence tells us it is working correctly? Who is accountable when it does not?
If your organization is moving AI from isolated pilots into enterprise applications, agents, or regulated workflows, contact our AI team to design governance architecture, technical controls, evaluation, and operating processes alongside the application itself.

 https://www.sotatek.com/
 (+84)2466585248




